Small businesses in Canton, Akron, Cleveland, and Youngstown face the same attackers as large companies, usually with a fraction of the security staff. The FBI's 2025 Internet Crime Report recorded $20.9 billion in reported losses nationally, up 26% from the year before, including 27,626 complaints and $421 million in losses from Ohio alone. Organizations that handle sensitive information or answer to regulators carry the most exposure.
- Financial impact varies: downtime, recovery, legal review, and fraud losses depend on the incident and the business.
- Closure claims need caution: the repeated “60% within six months” statistic has no dependable primary source.
- How attackers get in: in Verizon's 2026 Data Breach Investigations Report, exploiting a vulnerability was the most common first step (31% of breaches), ahead of phishing (16%) and stolen credentials (13%).
Attackers have intensified their focus on small businesses across Northeast Ohio for two main reasons: smaller organizations often lack comprehensive IT security and they are trusted partners or custodians of highly valuable customer, payment, and patient data. Modern attack methods go beyond spam or malware—they incorporate artificial intelligence, gather personal details from public records, and are fine-tuned to evade basic filters and antivirus software.
Small businesses now also contend with an expanding set of compliance requirements—HIPAA in healthcare, PCI-DSS for payment processing, and evolving state privacy laws. A breach can quickly become both a technical and regulatory emergency.
This article breaks down the most urgent cybersecurity risks Northeast Ohio small businesses face for 2026, why they matter, and how your organization can take practical, affordable steps to protect itself. All information is educational, and the prevention checklist near the end gives you a place to start. For legal or compliance-related guidance, always consult a certified expert.
1. AI-powered phishing and deepfakes
The changing face of phishing
Artificial intelligence has changed the way phishing works. No longer are these attacks limited to generic scam emails; now, cybercriminals use machine learning tools to craft messages and phone calls that convincingly imitate your trusted colleagues, leaders, or vendors. They can even clone voices and create audio deepfakes, making a fake “CEO” call nearly indistinguishable from the real thing.
- Definition: Attackers use AI tools trained on social media, company websites, or public data to send emails or make calls impersonating executives or staff. These messages often request urgent wire transfers, invoice changes, or login credentials.
- Examples:
- In 2024 an employee at the engineering firm Arup sent about $25.6 million after a video call in which the CFO and other colleagues were deepfakes, as the company confirmed to CNN.
- The FBI recorded more than $30 million in 2025 business email compromise losses where AI was involved, in its 2025 Internet Crime Report.
- Risks:
- Well-written scams with no malicious attachment can get past basic spam filters and antivirus.
- Breached email accounts, staff profiles on LinkedIn, and website directories supply attackers with names, roles, and communication styles.
Practical ways to defend your team
- Staff training: Run quarterly cybersecurity sessions, focusing on how to spot warning signs—odd requests, pushy urgency, or unusual banking instructions.
- Verification protocols: Always confirm high-value wire requests or sensitive data changes through a separate channel: a direct phone call to a trusted number, or a face-to-face check.
- Email security: Leverage affordable 24/7 IT security monitoring and protection tailored to small businesses, providing advanced filtering, sender verification, and impersonation detection.
Human judgment remains the most reliable line of defense. Training, layered verification steps, and updated security tools form a resilient combination against modern AI-powered threats.
2. Ransomware-as-a-service (RaaS) evolution
How ransomware has changed
Ransomware has become a packaged, outsourced “as-a-service” crime. Attackers lease ready-made attack kits, complete with customer support, and use them to target small organizations. No advanced hacking skills required—meaning more attacks, faster.
Most ransomware groups now steal data as well as encrypting it, then threaten to publish it. CISA calls this double extortion. Some add a third lever:
- Encryption: business files, and any backups the attacker can reach, are locked.
- Data theft: company and customer data is copied, with a threat to post it publicly unless paid.
- DDoS attacks: attackers threaten or launch denial-of-service attacks on your website to add pressure.
Extortion tactics: quick breakdown
| Element | What happens | Key defense |
|---|---|---|
| Encryption | Files & backups locked | Offline, tested backups |
| Data theft | Information stolen/leaked | Data encryption, segmentation |
| DDoS attack | Systems overwhelmed | Incident response plan |
- Total impact varies: Account for downtime, recovery, legal review, lost client trust, and rebuilding—not just a ransom amount.
- Cloud danger: Ransomware often seeks out and scrambles connected cloud storage and backups—online backups alone may not save you.
- Limited recovery: Corrupted, connected, or untested backups can prevent a complete restoration.
Your best defenses
- Air-gapped backups: Keep at least one backup fully offline and test it monthly. Reliable backup and disaster recovery solutions are available that fit both budget and regulatory needs.
- Rapid patching: Update remote access software and cloud services at least every week to close vulnerabilities.
- Endpoint detection & response: Employ EDR—more advanced than basic antivirus—to spot unusual file activity, ransomware behaviors, or mass encryption attempts.
A detailed disaster recovery strategy and tested incident plan help small businesses in Northeast Ohio minimize the cost and impact of these modern ransomware threats.
3. Supply chain attacks targeting small business partners
Risks in the supply chain
Small businesses increasingly rely on third-party software, cloud services, and vendor partnerships. Attackers know that compromising a single software provider or trusted contractor can create ripple effects.
- Attack paths:
- Hack a widely used vendor platform: criminals then access all client accounts at once.
- Steal contractor credentials, then use “trusted” remote access to breach your own network.
- How it plays out:
- In 2023 the Cl0p group used a previously unknown flaw in the MOVEit Transfer file-sharing product to steal data from organizations that relied on it, according to a joint CISA and FBI advisory.
- Breaches with a third party involved rose 60% in a year and made up 48% of all breaches in Verizon's 2026 report.
Vendor security for SMBs
- Assess vendor risks: Request security policies, incident histories, and regulatory compliance evidence before engaging with any third-party.
- Monitor continuously: Watch for odd vendor account logins and require notification about service changes or breaches.
- Revisit contracts: Make sure your agreements require vendors to maintain good security practices and notify you of any potential breaches quickly.
By treating every vendor connection as a potential entry point, you strengthen your business’s perimeter and reduce hidden risks.
4. Insider threats and human error
The role of people in cyber incidents
Not all breaches come from outside. In many small businesses, employees and contractors unintentionally cause issues by clicking phishing links, misconfiguring software, or using weak passwords. Sometimes, insider threat is intentional—motivated by dissatisfaction or the opportunity for financial gain.
Common triggers:
- Mistakenly opening attachments with malware
- Allowing default or simple passwords for sensitive logins
- Mismanaging file permissions so confidential documents are left public
- Employees or contractors with unmonitored access—especially after leaving the business
Regulatory impact:
- For healthcare, legal, finance, and payment processing organizations, mistakes can turn into HIPAA or PCI DSS problems. HIPAA civil penalties are set per violation and adjusted for inflation each year (HHS enforcement); PCI consequences come from your card processor's contract rather than a public fine schedule.
Preventive actions
- Ongoing security training: All staff, especially those handling private data, should receive updated cyber-awareness training every quarter.
- Role-based access: Only give staff access they absolutely need, and promptly remove permissions when roles change or people leave.
- Tested response plan: Prepare and rehearse proper steps in the event of a breach, including legal notifications and customer communication.
Note: Always consult with a compliance specialist for regulated fields. Informational guidance is not a substitute for legal or certified compliance advice.
5. IoT and endpoint vulnerabilities
Weakest links in the office
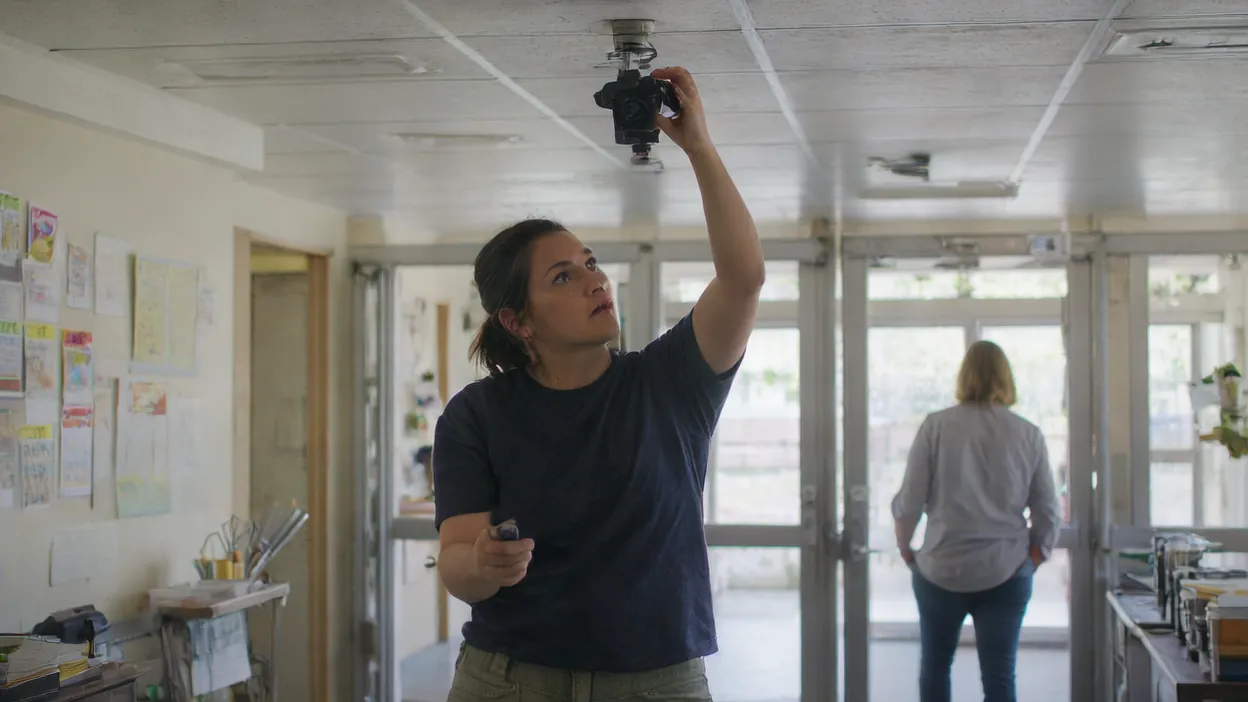
Internet-connected devices, or IoT, are found everywhere in Northeast Ohio offices—thermostats, security cameras, printers, and even door controls. These often come with manufacturer-default passwords or outdated firmware, creating large holes in business defense.
- Vulnerability examples:
- An adversary logs into an unlocked printer and uses it to enter your core network.
- Smart security cameras are hijacked and used to track network activity.
- HVAC controls left open to the internet become a backdoor to business systems.
- Business impact: Once inside through an IoT device, attackers may access confidential records, disrupt business operations, or even breach compliance.
Local steps for strong protection
- Endpoint security: Invest in endpoint protection services that monitor both computers and IoT devices for abnormal activity.
- Segment networks: Place IoT systems on separate networks (VLANs); never mix with payment or patient information systems.
- Update firmware: Set reminders for regular updates of every device connected to your business network—missing just one can open the door.
Partnering with Northeast Ohio professionals means you receive hands-on help identifying and securing every device, tailored to your exact setup.
6. Quantum-resistant cryptography challenges
Big changes on the horizon
A large enough quantum computer could break the public-key encryption (RSA and elliptic-curve) that protects email, file transfers, and payment systems today. No such machine exists yet, but data stolen now could be decrypted later, which matters for businesses that keep sensitive records for years, such as healthcare, legal, and finance. NIST published the first finalized post-quantum encryption standards in August 2024.
- What’s at stake:
- Encrypted data captured today could be read once quantum computers are capable enough.
- Vendors and regulators are starting to plan the move to the new standards, so expect it to show up in software updates and, eventually, compliance requirements.
How to begin preparing
- Professional evaluation: Use expert technology consulting services to review your systems for vulnerable encryption protocols and prioritize upgrades as needed.
- Upgrade over time: Replace old encryption standards with quantum-safe versions as your hardware and software vendors release verified updates.
Monitoring industry compliance trends and planning ahead protects your business from being caught unprepared as cryptography requirements change.
7. Zero-day exploits in cloud services
Defending against the unknown
Cloud services power a huge portion of Northeast Ohio’s small business operations. Yet, “zero-day” vulnerabilities—flaws unknown to software vendors until after criminals find and use them—create tough-to-detect risks.
- How zero-days work:
- An attacker discovers a new bug and exploits it before an official fix is available.
- Breaches may occur for days or weeks before suspicious activity is detected.
- Recent examples:
- The 2023 MOVEit Transfer campaign used a flaw nobody had patched yet, because nobody outside the attackers knew it existed (CISA advisory).
- Verizon's 2026 report found organizations fully fixed only 26% of the critical flaws on CISA's Known Exploited Vulnerabilities list, taking a median of 43 days. Known holes stay open far longer than true zero-days.
Key safeguards
- Active patch management: Check for and apply updates to all cloud apps weekly—or sooner if irregular activity is publicized.
- Managed security and monitoring: Choose IT services that focus on cloud defenses, like anomaly detection and real-time attack alerts.
- 24/7 monitoring: A watchful eye means threats can be contained quickly, minimizing business and compliance risk.
Northeast Ohio organizations benefit from local providers capable of fast, in-person response—ensuring cloud and physical systems stay reliably protected.
General prevention strategies for small businesses
2026 security action checklist
Prioritize these proven steps to create a layered, manageable defense tailored to small business realities:
- Quarterly security training: Refresh all staff on the latest phishing tactics, AI-driven scams, and evolving compliance rules.
- Multi-factor authentication (MFA): Set up for every high-value system and sensitive account, especially executives and financial users.
- Tested offline backups: Keep copies of critical data air-gapped—unplugged and off-site if possible. Test recoveries monthly.
- Weekly patching: Schedule system, device, and application updates every week; patch more frequently if emergency advisories appear.
- Endpoint detection & response (EDR): Use tools that analyze patterns and isolate hacked computers or devices, stopping threats that slip past standard antivirus.
- Annual penetration testing: Hire local experts to simulate attacks and find gaps in defenses before criminals do.
- Impersonation safeguards: Develop executive “code words” and a call-back process for wire transfers or sensitive decisions. Require verification of unusual requests verbally, not by email alone.
- Security documentation: Maintain, review, and update basic security policies. Ensure all staff know how to report suspicious incidents and where to find protocols.
Making cybersecurity a routine business process—and using services built for small business budgets—reduces both financial and compliance risk.
Ready to strengthen your small business security?
Protecting your small business from today’s advanced cyber threats does not require enterprise budgets or endless contracts. NHM Ohio is built around the Northeast Ohio business community, providing affordable, transparent, and locally delivered IT security and managed services designed for real needs.
Start building your cyber defense today:
- Try our free domain security checkup tool and uncover email weaknesses or authentication errors before they become costly.
- Have questions about ransomware, compliance, or cloud security? Contact NHM Ohio for a free consultation and we'll talk through what your business needs.
Informational note: This content is for education and awareness only. It reflects reported industry trends, not absolute guarantees or certified compliance guidance. Always seek a certified specialist for legal or regulatory security needs.
Frequently asked questions (FAQ)
Why are small businesses prime targets in 2026?
Attackers focus on small organizations because they often have less comprehensive IT defenses, but still handle valuable data (such as payments, health records, or business contracts). Many also link to larger companies through vendor chains.How do AI deepfakes differ from traditional phishing scams?
AI deepfakes use voice cloning, customized language, and public company information to convincingly impersonate known contacts, making attacks much more believable than generic phishing emails.Can free antivirus protect against modern ransomware?
Basic antivirus is built mainly to catch known malicious files, and it can miss new or customized variants. EDR software watches for suspicious behavior, can isolate a machine, and is usually monitored by someone, which makes it a much stronger layer.What is the average cost of ransomware attacks on SMBs?
There is no useful universal average. Total impact can include fraud or ransom, system recovery, business interruption, legal review, notification, hardware, and possible regulatory consequences.How often should backups be tested against ransomware?
At minimum, monthly. Restoring from backups regularly ensures you can recover quickly, even if online backups are encrypted or wiped during an attack.Can a cyberattack put a small business out of business?
It can, but nobody has a reliable closure rate, and the popular "60% close within six months" figure has no source. What is measured: in Verizon's 2026 Breach Impact Study, the worst breaches (the top 2.5%) cost small and mid-sized businesses more than 7% of revenue. Recovery costs, lost customers, and compliance penalties add up fastest for businesses that are not prepared.What verification steps help stop CEO deepfake scams?
Require a call-back or in-person confirmation for any sensitive requests, use codewords among leadership, and always verify banking info changes independently.Is MFA enough against AI-enhanced attacks?
MFA is an essential security control, but cannot prevent all attacks—especially voice or text-based social engineering. Combine it with training, verification checks, and incident response plans.How has ransomware evolved recently?
Most groups now steal data as well as encrypting it (double extortion), and some add a third lever, threatening denial-of-service disruptions if payment isn’t made.What EDR features benefit small businesses compared to free AV?
EDR tools monitor for abnormal behavior, isolate compromised systems, and support fast recovery. Basic antivirus does less of this and is more likely to miss new, targeted attacks.
For independent guidance or rapid support, NHM Ohio offers effective, cost-aware IT security for Northeast Ohio small businesses—rooted in local expertise and real-world solutions. Reach out for a personalized security review and make cybersecurity a business advantage, not a source of stress.